Extend Your Stack
Without Replacing It
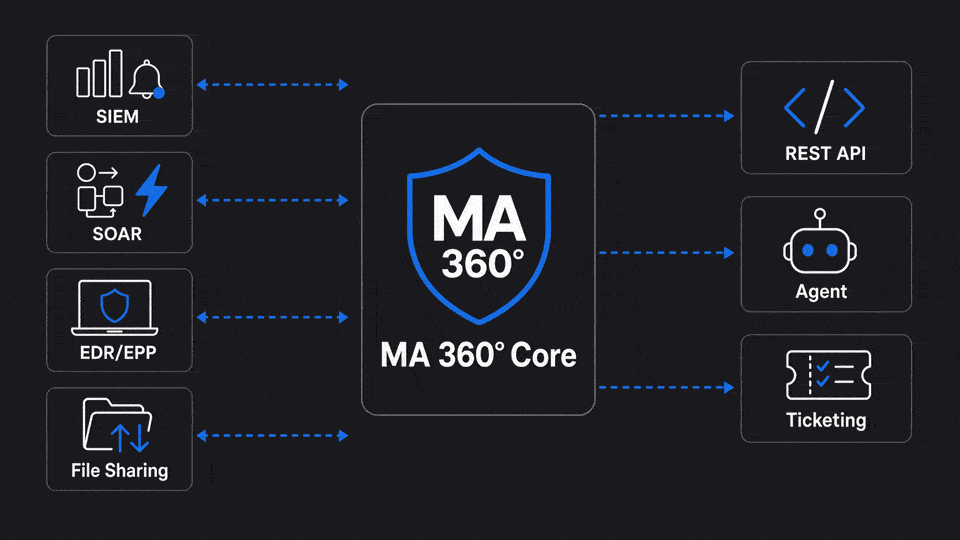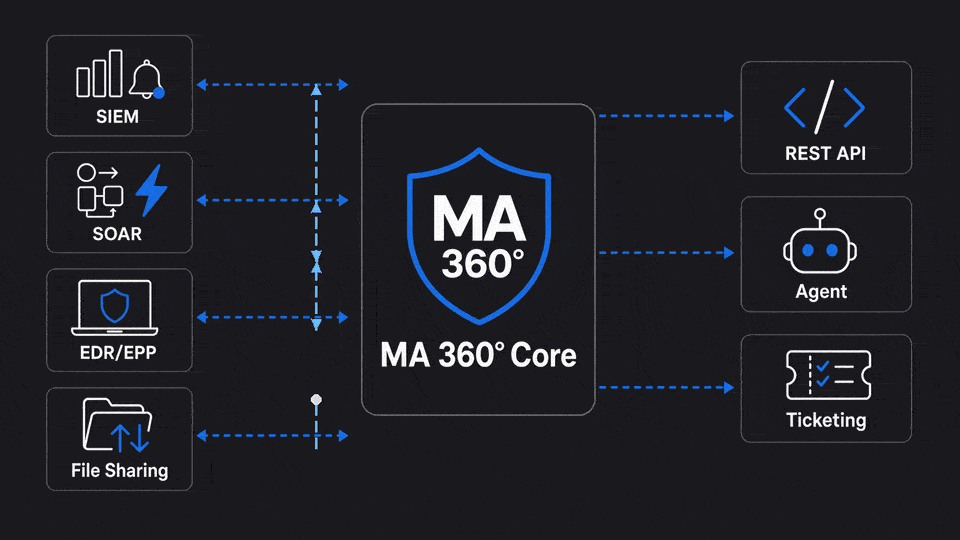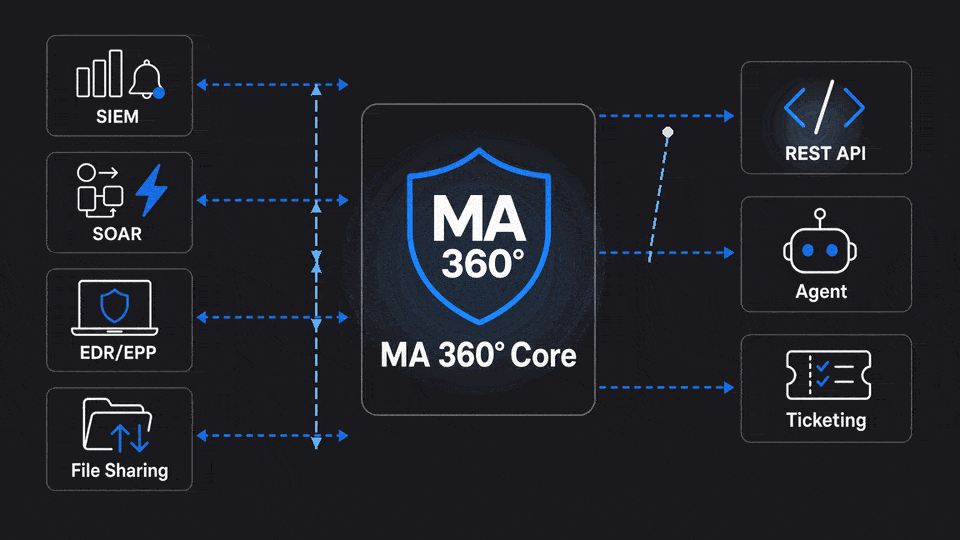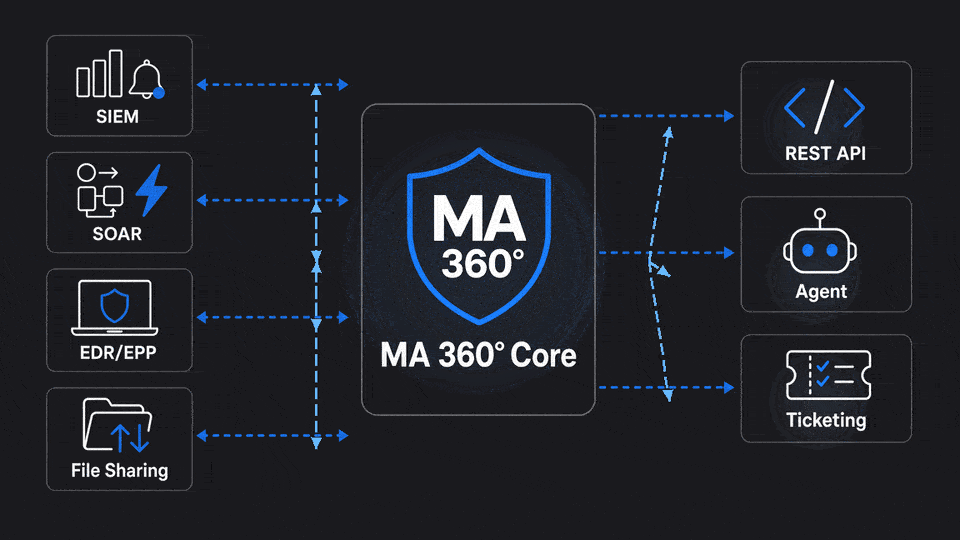
CyberFortress is built on a fully open architecture. The point is not to become your only security vendor – it is to make the tools you have already paid for work harder.
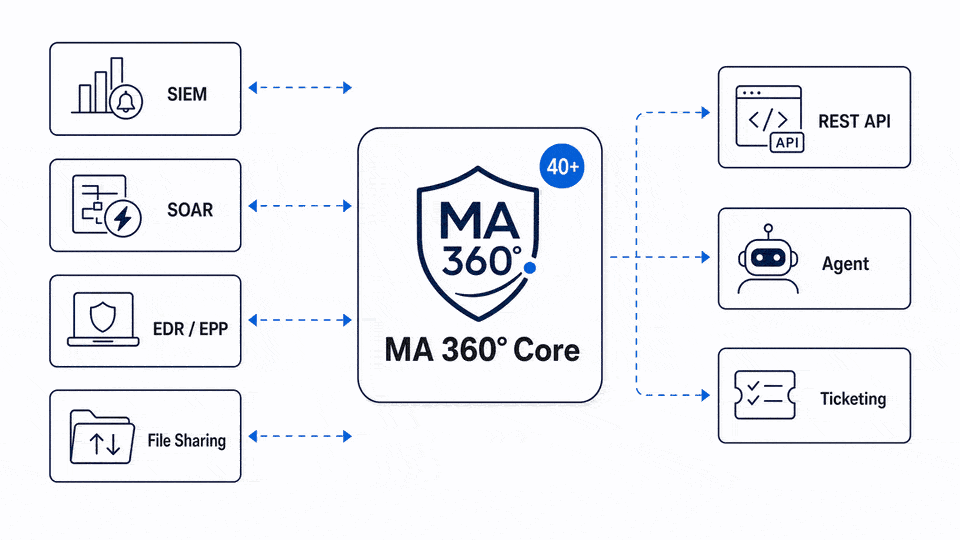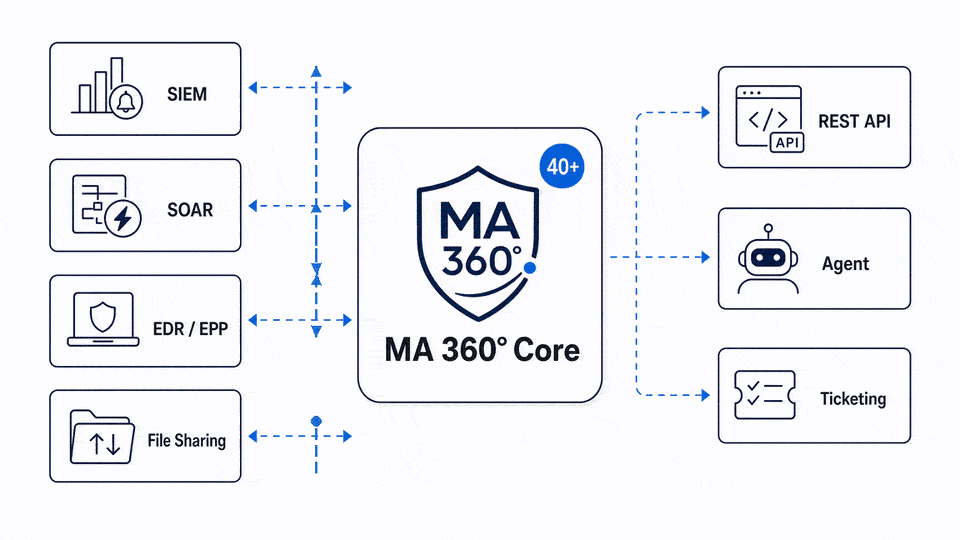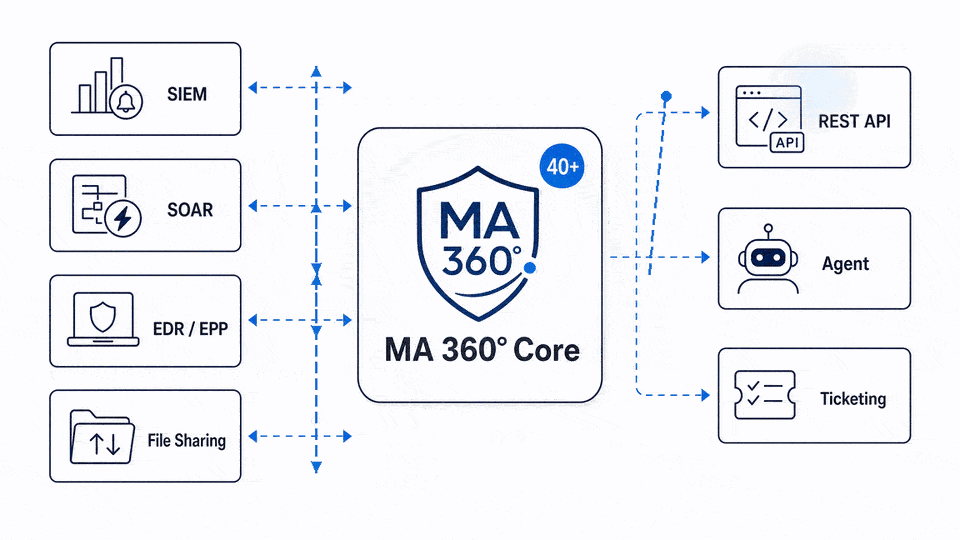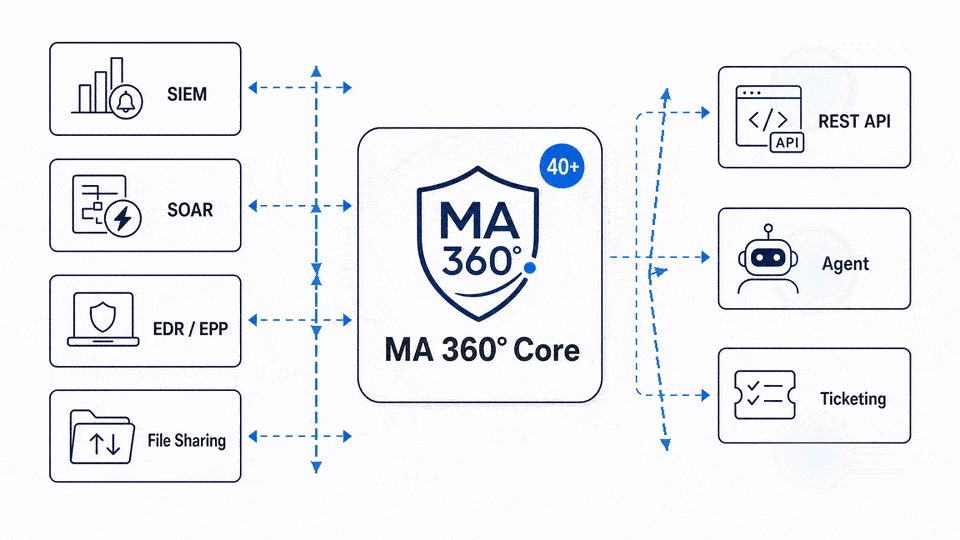
Lightweight agents collect from endpoints with a minimal footprint, and a RESTful API connects the engine to more than 40 security tools with bi-directional data flow.
40+
Security tools with ready integrations
REST
Full RESTful API for custom automation
2-way
Bi-directional data and action flow
Light
Minimal-footprint agents, maximum visibility
What connects
Threat data, event records, alerts and automation actions stay synchronised across the whole ecosystem.
SIEM
Alerts, enriched incidents and extracted IOCs flow into your existing SIEM, so the security data lake stays authoritative and your existing dashboards keep working.
SOAR
An alert can trigger a playbook automatically – and the playbook can call back into MA 360° to isolate an endpoint or push a file to the sandbox.
EDR / EPP
Verdicts are shared in both directions, so a detection in one product becomes protection across the estate rather than an isolated finding.
Ticketing
Incidents open, update and close in your service desk automatically, keeping the audit trail where your processes already live.
File sharing
SharePoint, OneDrive and file shares submit uploads for analysis before a file is stored or opened by anyone else.
Custom via REST API
Anything not on the list can be wired up directly – submit files and URLs, pull verdicts and reports, and drive actions from your own tooling.
Integration is not just data sharing
Moving records between systems is the easy half. The value shows up when the connection carries actions as well as data, and manual steps start disappearing from your runbooks.
A single alarm from the SIEM can trigger a SOAR playbook; at the same moment MA 360° isolates the affected endpoint and sends the suspect file to the sandbox. What used to be a sequence of human handoffs becomes one orchestrated response.
1. SIEM raises an alarm on anomalous outbound traffic.
2. SOAR playbook fires automatically.
3. MA 360° isolates the endpoint and submits the file.
4. Sandbox returns a verdict with IOCs and ATT&CK mapping.
5. IOCs push to EDR and firewall; the ticket updates itself.
Two ways in
Agent-based collection and API-based integration solve different problems, and most estates use both.
Connect it to what you already run
Tell us your stack and we will show you exactly which integrations apply and what the automation looks like end to end.